Risks and the heat map
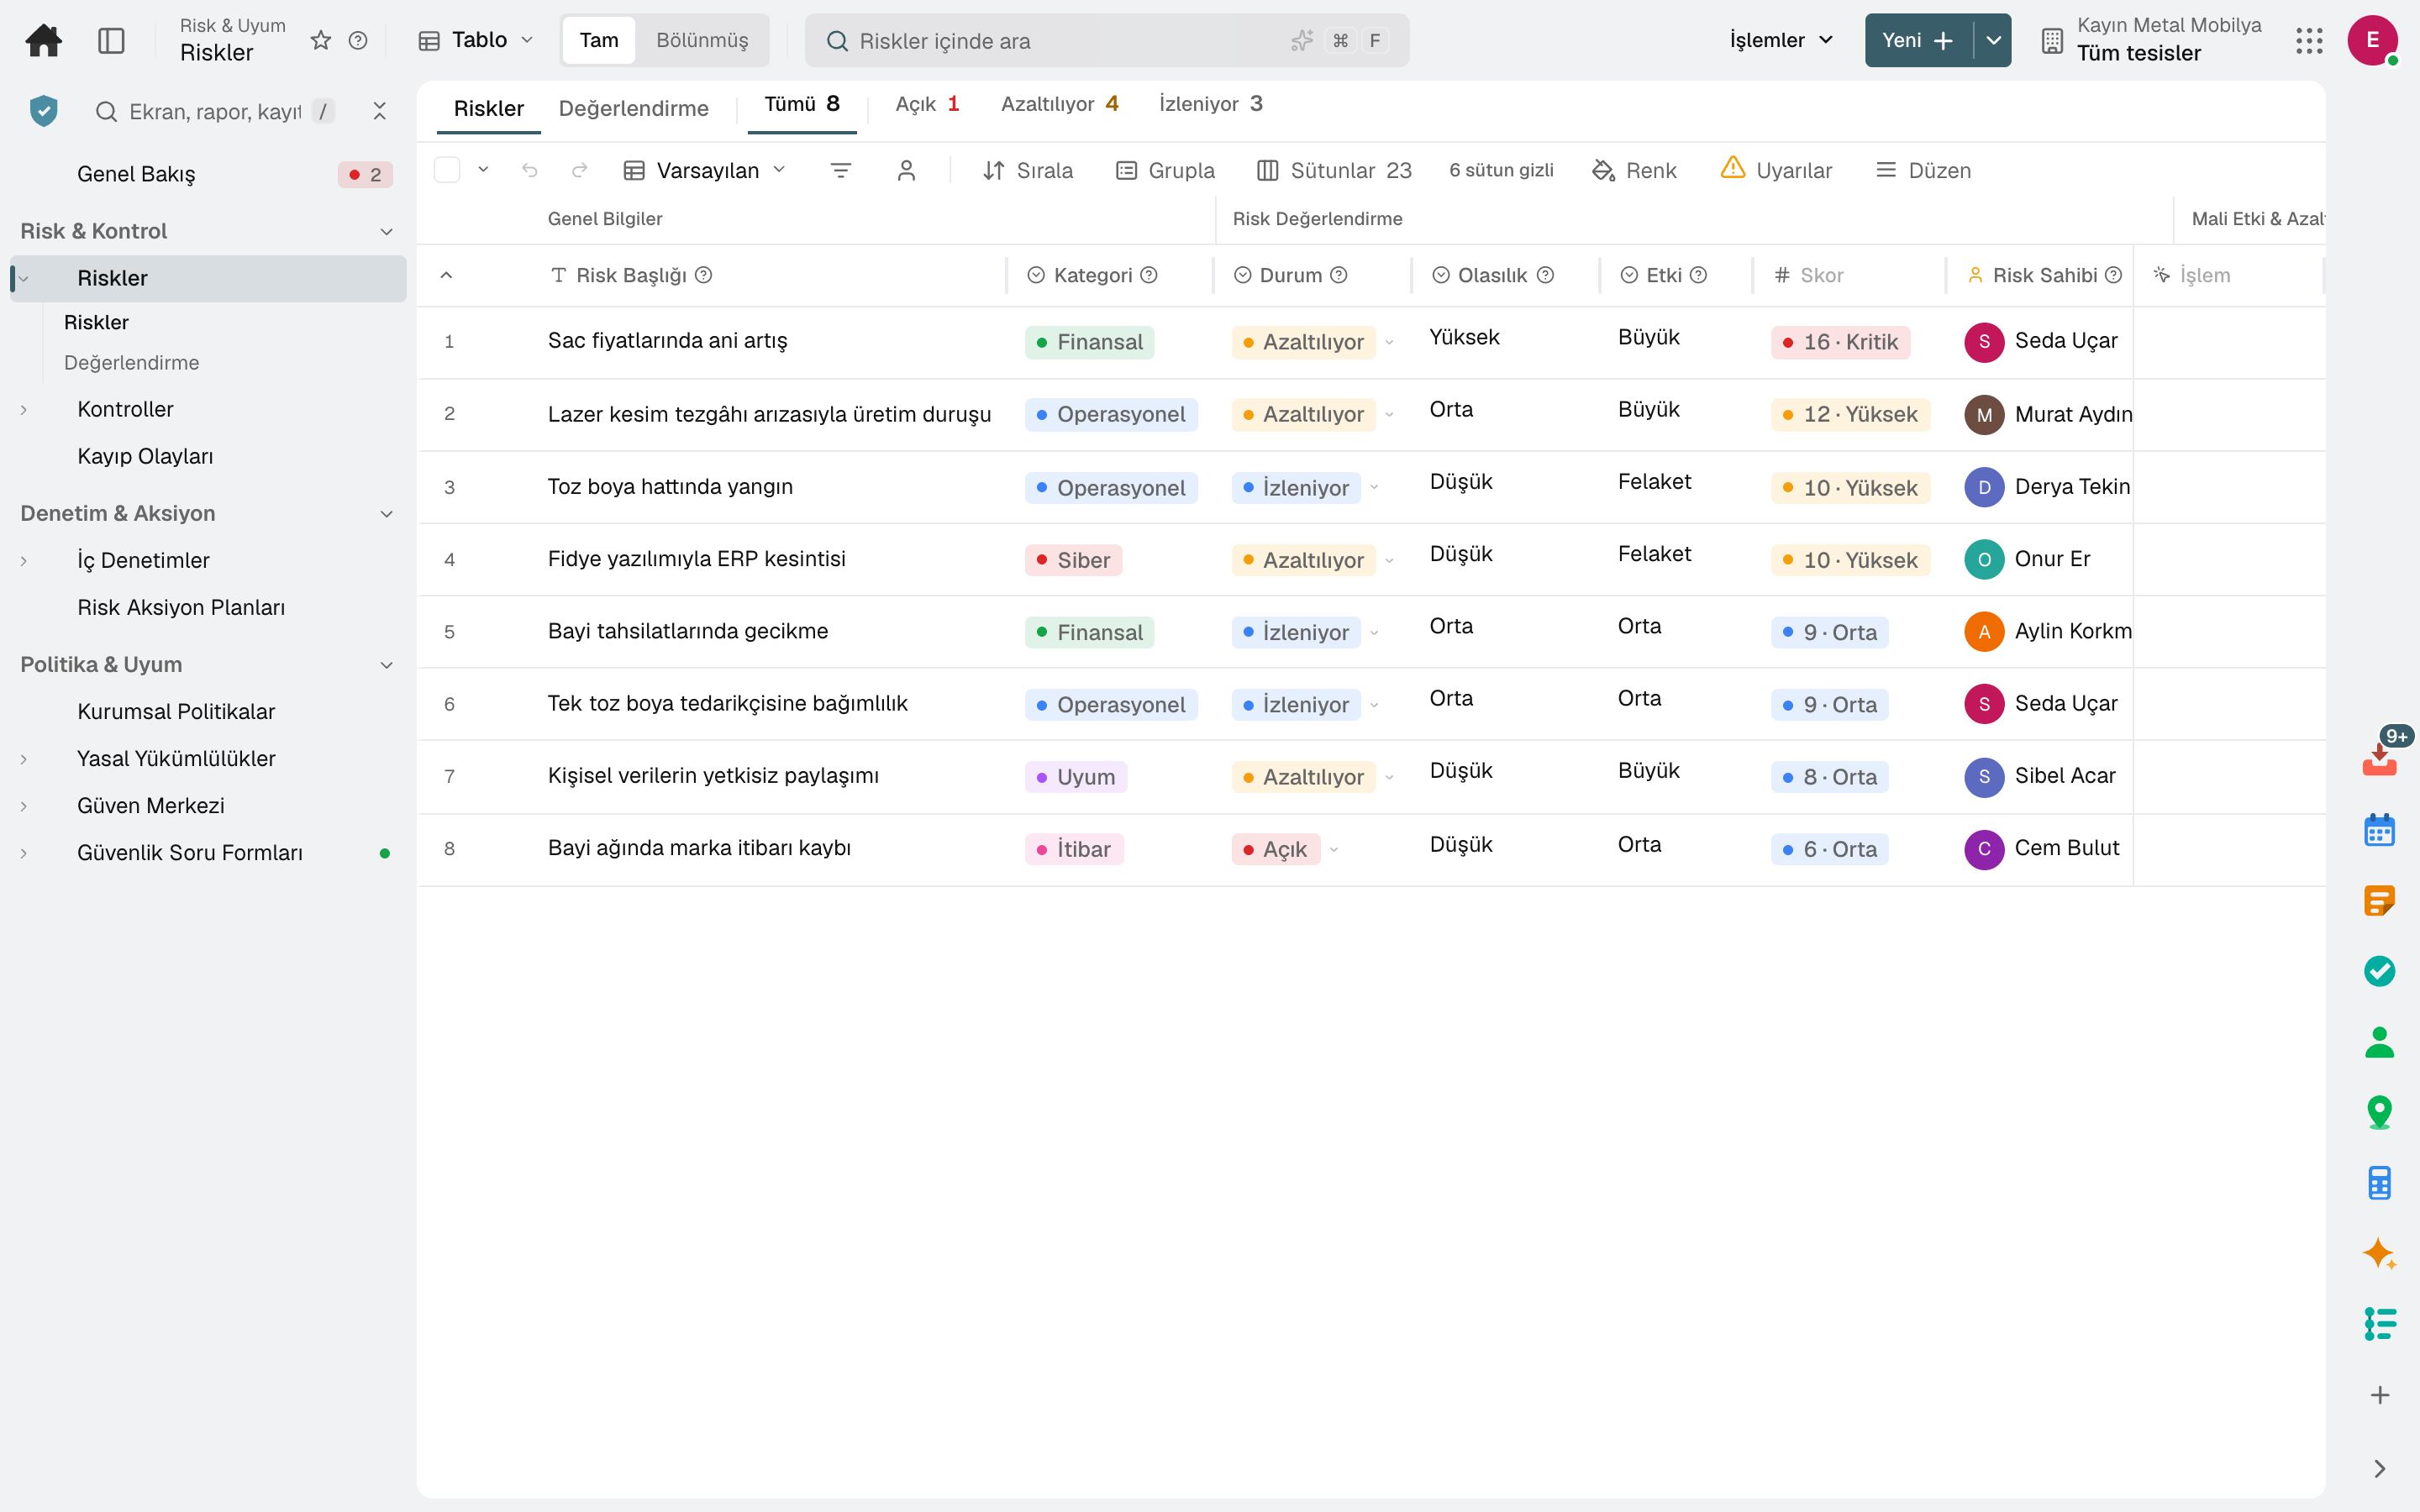
Risks with owner, score and mitigations; a probability and impact heat map, periodic reassessment.
Enterprise risks and the heat map, internal controls and their tests, internal audits, policies, risk action plans, loss events and anomaly monitoring in one app.
What is it, and why do you need it?
When the risk list lives in a spreadsheet updated once a year and audit findings stay in a report, nobody knows whether the actions were closed until the next audit.
Risk & Compliance links every risk to its owner and score, every control to its test and every finding to its action. Anomaly monitoring continuously scans transaction data for rule violations.
Scope: Runs the risk matrix, controls, audits and compliance (governance) processes.
Highlights
Risks with owner, score and mitigations; a probability and impact heat map, periodic reassessment.
Controls that mitigate risks and their owners; control tests and their results.
Audit planning and execution; findings are tracked with corrective actions until closure.
Corporate policies are published and acceptance is tracked.
Loss and breach events are recorded and their resolution is tracked.
Rule violations and anomalies in transaction data are monitored continuously.
Business impact analysis of processes, recovery plans and exercises; an exercise finding becomes an action.
The country's obligation catalogue (permits and registrations, periodic inspections) and a compliance plan per site; gaps land in the task inbox and the calendar.
The security page a customer or auditor sees without creating an account: certificates, documents, subprocessors and FAQ; confidential documents open on an access request.
Sub-modules
This list is generated from the product itself; it grows as new functions are added to a sub-module. Master data and settings are the shared ground of every module and are not counted as sub-modules.
On the same data
Modules are separate screens, but the data is one: a record entered in one module is never re-entered in another.
Users, permissions, definitions and integrations on one admin screen.
No missed contract expiry, no missed hearing.
Board decisions, shareholders and dividends on record.
In the journal the moment the invoice is issued; no waiting for month end.
Frequently asked
Every finding is linked to an action plan and its owner; it stays on the open list until the action is closed.
Yes. A policy is published, and who has accepted it is listed.
The transaction data across all modules; a record is created when a defined rule is violated.
Try it free for 15 days; no credit card needed. We reply to your questions within one business day.